
Secure Sharing on Your Own Terms
A secure upload link for clients is something you buy from a vendor you simply have to trust. Not anymore. Cryptly shows the other way.
Every bookkeeper, accountant and lawyer knows the question: "Could you send that over securely?" Annual accounts, a passport copy, a draft contract. Email won't do, so there's a portal. Bought from a vendor, as a managed service, often priced per user per month.
That moves the problem. It doesn't solve it.
Trusting the brochure
A service like that promises everything is encrypted. That nobody is looking. That files disappear after a while and everything stays in Europe. You can't check any of it. You read the brochure, sign the data processing agreement and assume it holds.
Meanwhile your clients' most sensitive documents sit with a third party. They set the retention period. They set the price. They decide whether your client has to create an account before sending a single PDF. And if they get acquired tomorrow, or change the terms, you follow.
That's where control starts leaking.
What you can't read, you can't leak
It can be done differently, and we've shown it. Cryptly does two things: send something sensitive, or request something sensitive. A password, a note, a PDF.
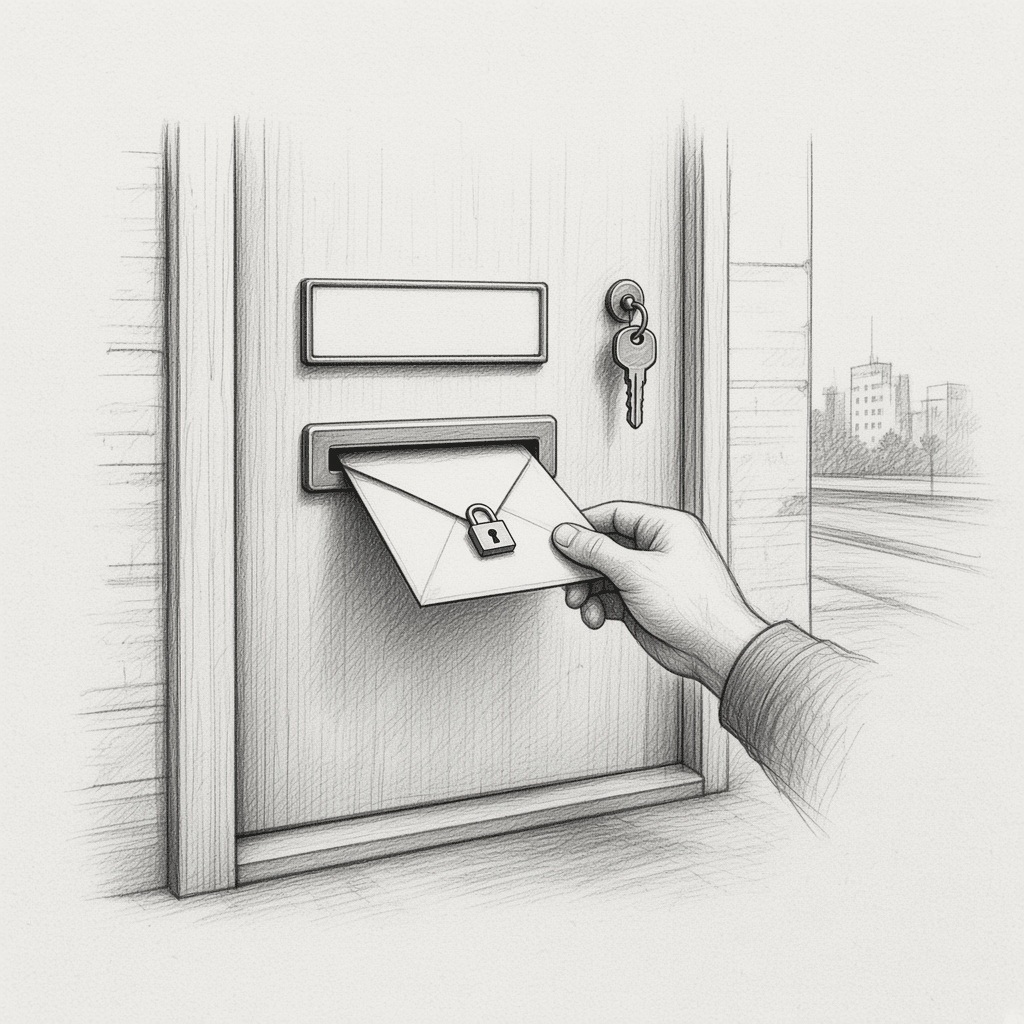
Think of an envelope with a lock on it. The sender's browser locks the file before it leaves the computer. The server only keeps the sealed envelope. The key sits in the link itself, in the part after the hash sign, and a browser never sends that part to a server.
The link opens once. After that the file is gone. Never picked up? Then the link expires on its own, for a file within three days at most. Nobody needs an account. Your client gets a link, picks a file and is done.
The difference with the brochure: you don't have to take anyone's word for it. The server holds encrypted data only. We can't read it. Neither can the party hosting the database. And whoever steals that database gets nothing useful.
The trust is in the design. Not in a promise.
Your name on the front door
Cryptly is a showcase. You don't have to use our service to see the point: services like this are no longer reserved for specialized vendors.
The same setup runs just as well on your own domain, in your own branding. You decide how long a file stays, how large it can be and which country the server is in. No price per user. No one else's logo between you and your client.
And you serve the code that does the encrypting yourself. So nobody sits in between who could quietly change it.
A few years ago this was a serious IT project. Not anymore. You can just build things.
Being able to isn't a reason
Still: don't build everything you can build.
Cryptly needed a lot besides the encryption. Limits against abuse. A place to report misuse. Daily cleanup. A privacy policy that matches what the software does. Own a service and you own its upkeep.
So the question is what's core and what's edge. You don't write your own accounting package. But for an accountant or a lawyer, confidentiality isn't an edge. It's what the client comes for. How their documents reach you is part of the service.
My advice: choose deliberately. Buying is fine, if you know what you're handing over and to whom. Just stop assuming that buying is the only option.
That time is over.